Why There's No Customer Logo Wall Here
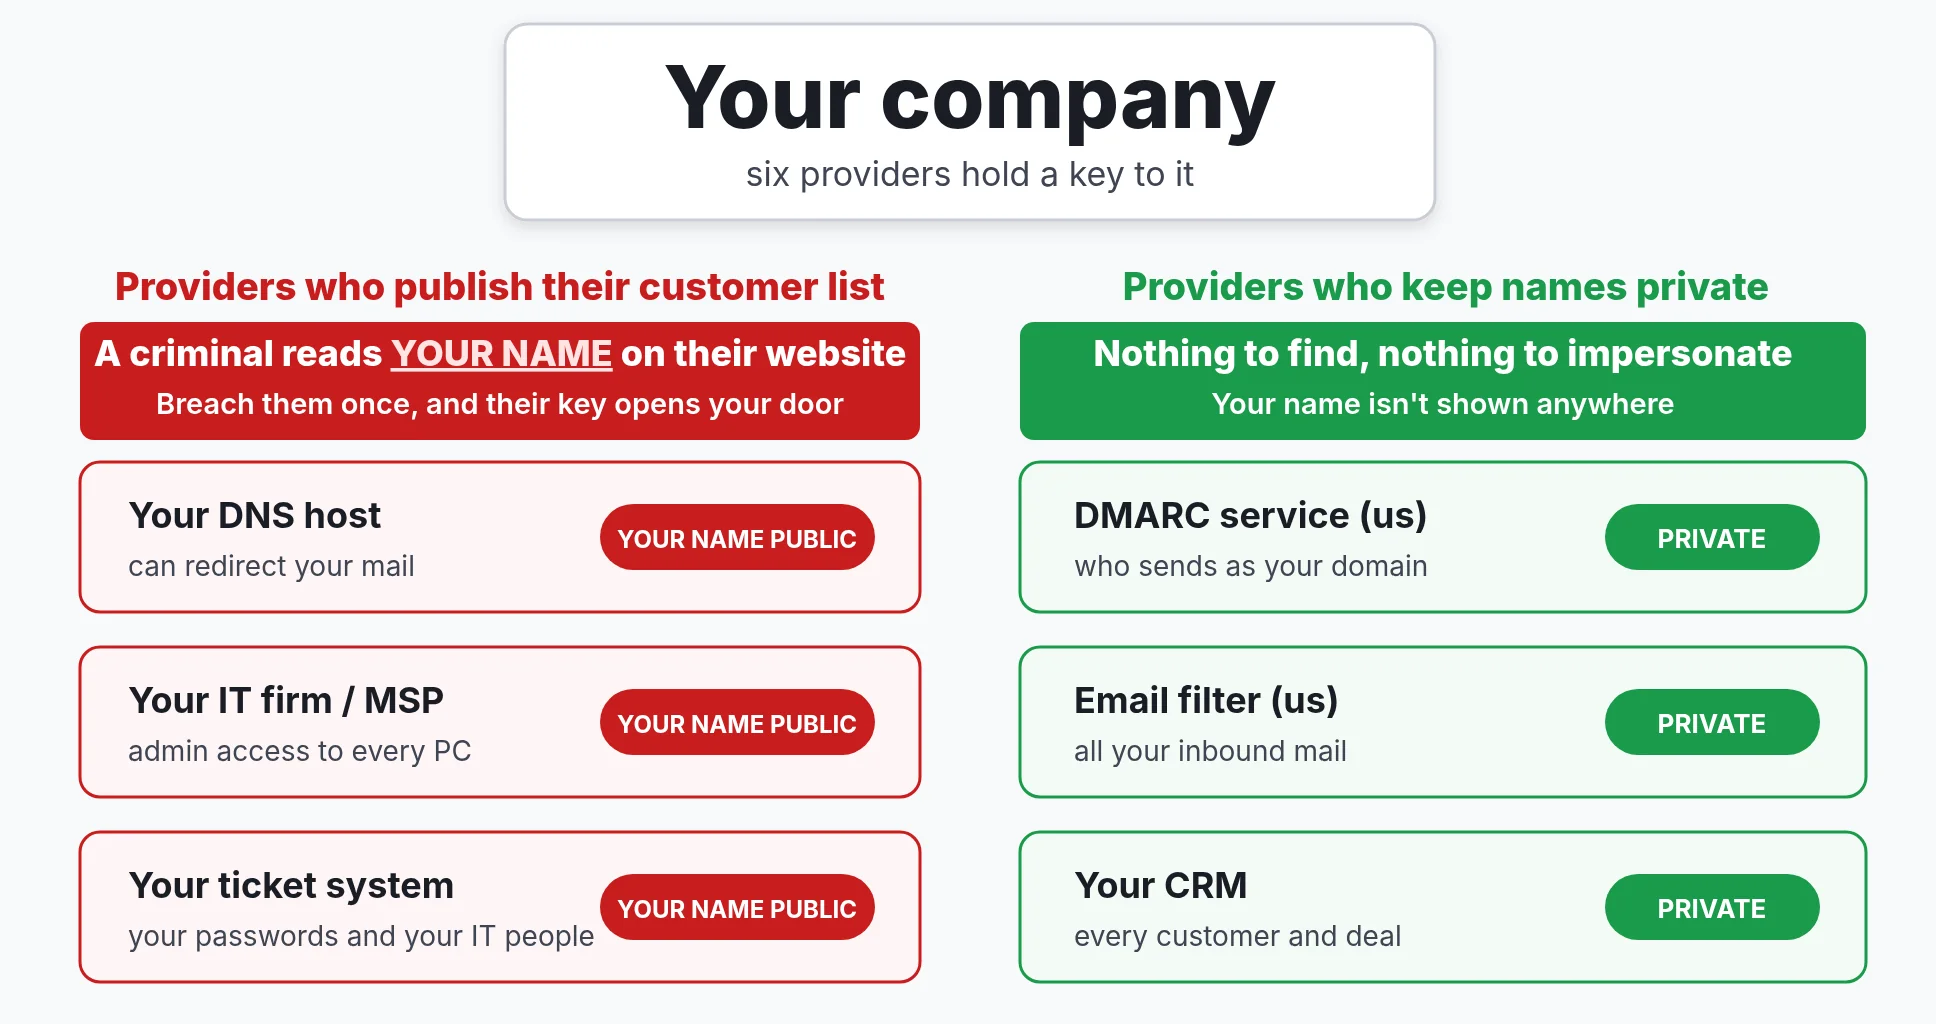
Many providers show a row of customer logos to look trustworthy. We don't, on purpose.
LastSpam sits in front of your inbox: every message to your organisation passes through us before it reaches you. DMARC Guy, the same team, reads the reports that say who sends email as your domain. A company that holds a piece of your infrastructure should not be advertising whose infrastructure it is.
What a logo wall tells an attacker
Nobody breaks into a well-defended company through the front door. They go through a provider that already has a key. The first step is finding out which providers those are, and vendor websites answer that question for free.
- Who is reachable through this vendor. Fifty logos on one page is a list of fifty organisations that all share the same door. Compromise the vendor once, and every name on the wall is on the other side of it.
- Which emails your staff will trust. If it's public that you use a given mail filter, CRM or ticket system, a forged "notification" from that brand looks normal to your people. No breach of the vendor needed; the name alone does the work.
- What access that vendor holds. Each provider type implies a known kind of access: DNS login, admin role in your tenant, API token, remote-control agent. Name the vendor and you've named the key.
Every provider that names you is one more door with your name on it
This is a common practice, and an avoidable one. Here is what each kind of provider typically holds about an organisation, and what a public "they are our customer" hands to someone planning an attack.
| Provider | What they usually hold | What a public listing gives an attacker |
|---|---|---|
| Email filter / MX← us | Your entire inbound mail stream, often an admin connector in Microsoft 365 or Google | A forged quarantine digest or "release this message" link that looks exactly right |
| DMARC / email-auth service← us | Records in your DNS, your aggregate reports: a map of everything that sends as your domain | Which sending platforms you use, and a brand to impersonate for a "fix your DNS" request |
| DNS / domain host | Login that can redirect your mail and website | Knows which registrar's password reset to phish; a fake "renew your domain" email from the right brand |
| CRM | Every customer, contact and deal you have | The export worth stealing, and the login page to clone |
| ERP | Suppliers, bank details, invoices | The raw material for invoice fraud: who you pay, how much, when |
| Ticket / help-desk system | Internal problems, passwords pasted in tickets, who your IT people are | A believable "your ticket #4821 was updated" lure to the exact people who handle access |
| Mass-email platform | Your subscriber list and the right to send as your domain | Knows which platform to compromise to mail all your customers as you |
| IT consultant / MSP | Admin credentials and a remote-control agent on every machine | The single most valuable target: one firm, all of its clients at once |
| Backup provider | A full copy of everything | Where to go for the data when the live systems are locked down |
Six providers, six doors. If three of them published the relationship, three doors have your name on them before anyone has touched a keyboard.
This is how it actually happens
- Kaseya, July 2021. One remote-management vendor used by IT firms was compromised. Kaseya's own assessment: fewer than 60 direct customers hit, up to 1,500 businesses downstream, most of them clients of small IT providers. A Swedish grocery chain closed about 800 stores. Source
- SolarWinds, December 2020. Days after its software-update breach became public, the company removed the page listing its customers, which had named more than 425 of the Fortune 500. The archived copy is still online, which is the point: once published, a list cannot be taken back. Source
- Okta, January 2022. The attackers never broke into Okta's own network. They took over a laptop at a support subcontractor, and that session had enough access to Okta's support tools to reset customers' passwords. Okta first warned that up to 366 customers could be affected; the final count was two. The mechanism is the lesson, not the number. Source
None of these started with the victim's own network. All of them started with a provider that already had a key.
What we do instead
No names, anywhere. Not on this site, not in a slide deck, not in a case study without the customer's own written choice to be named. We treat your name the way we treat your mail.
References on a call. Want to talk to someone who uses us? Press the green button at the top of this page. We'll put you in touch with a customer who has agreed to take the call, one to one, nothing published.
What we can say. LastSpam has filtered business email since 2002, for firms, school boards and public bodies in Québec, Canada and the United States. The live threat map on our home page shows today's traffic as it happens, not a logo. DMARC Guy, the same team, handles email compliance and delivery problems for organisations from a few mailboxes up to 40,000 accounts. For the rest, ask us on a call.
Three questions to ask any provider
Not just us. Your DNS host, your IT firm, your CRM, anyone with a key.
- Do you publish your customers' names anywhere, including sales decks and social media?
- Who on your side can see our name, our data and our access, and how is that reviewed?
- If you were breached tomorrow, what exactly could someone do to us with what you hold?
A provider that answers all three without hesitation is one you can keep.
Talk to the person who runs it
The button at the top of this page is green when Jeff is available for a live video call, amber when he's already on one, and grey when he's away. Grey sends you to the contact form. Either way you reach the person who runs LastSpam, not a sales desk.
Jean-François Bourdeau · LastSpam · DMARC Guy · Montréal, Québec. Email security since 2002.